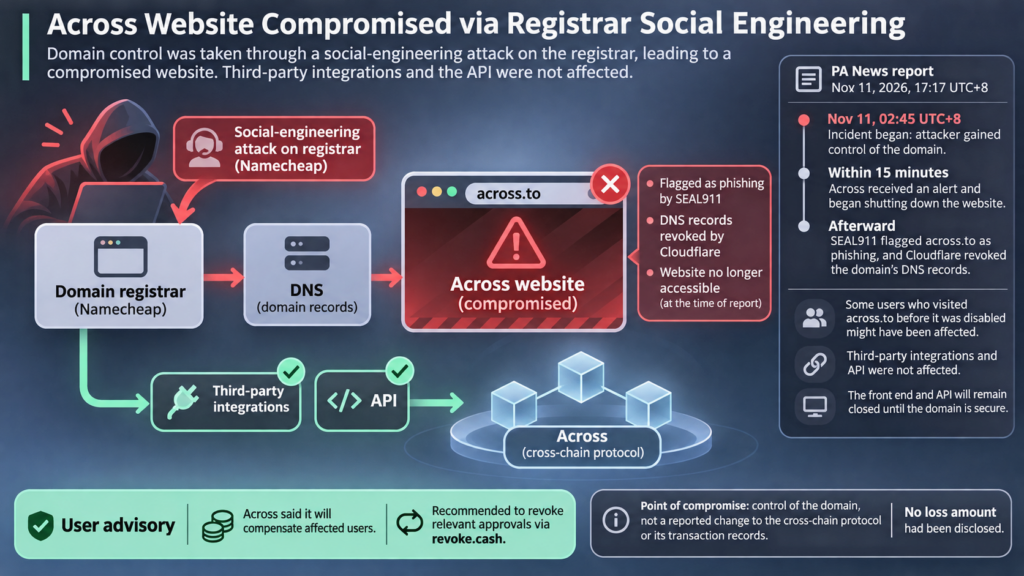
A cross-chain protocol’s website can be compromised without a reported change to the protocol itself. In a report published on November 11, 2026, at 17:17 UTC+8, PA News cited Across as saying an attacker gained control of its domain after a social-engineering attack on its registrar, Namecheap.
According to Across, the incident began at approximately 02:45 UTC+8 on November 11. The team received an alert within 15 minutes and began shutting down the website. SEAL911 subsequently flagged across.to as a phishing site, and Cloudflare revoked the domain’s DNS records. The phishing site was no longer accessible at the time of the report.
Across said some people who visited across.to before it was disabled might have been affected, while users of third-party integrations and its API were not affected. It said it would compensate affected users and advised them to revoke relevant approvals through revoke.cash. Across also said its front end and API would remain closed until the domain was secure. No loss amount had been disclosed.
The reported point of compromise was control of the domain, not a reported change to cross-chain transaction records. The source provides no transaction-level evidence from which to establish which users lost funds or how much they lost.
Source: panewslab.com (originally published 2026-11-11 17:17 UTC+8)